
authshore
Provides authentication infrastructure for coding agents, enabling user pool management, encrypted secrets storage, and JWT token operations through MCP tools.
README
as


Auth infrastructure for coding agents — user pools, secrets vault, token management. As easy as git.
git for your code. as for your auth.
Your agent can scaffold a whole app in an afternoon — then stalls the moment it needs auth. It hardcodes secrets into .env files it later commits, rolls its own JWT handling, and leaves you wiring up Cognito by hand. AuthShore is the auth layer your agent runs itself: one install, and it provisions user pools, stores secrets encrypted, and mints, validates and refreshes tokens — from the terminal, with no console to click through.
Works with: Claude Code · Cursor · Cline · Windsurf · Aider · Codex · any MCP client
See It In Action
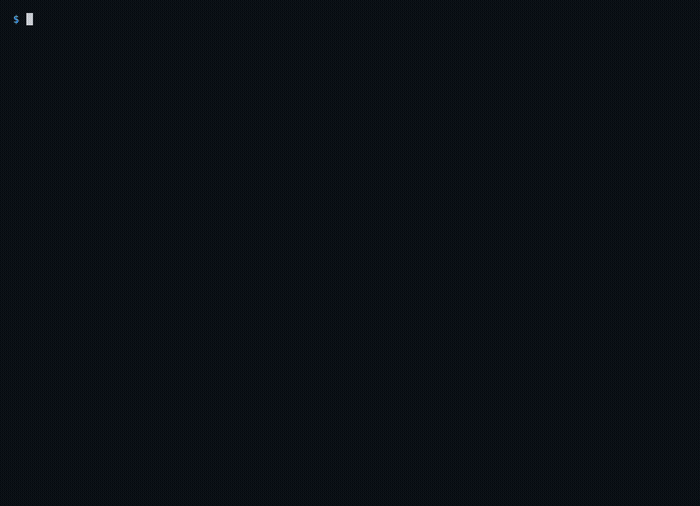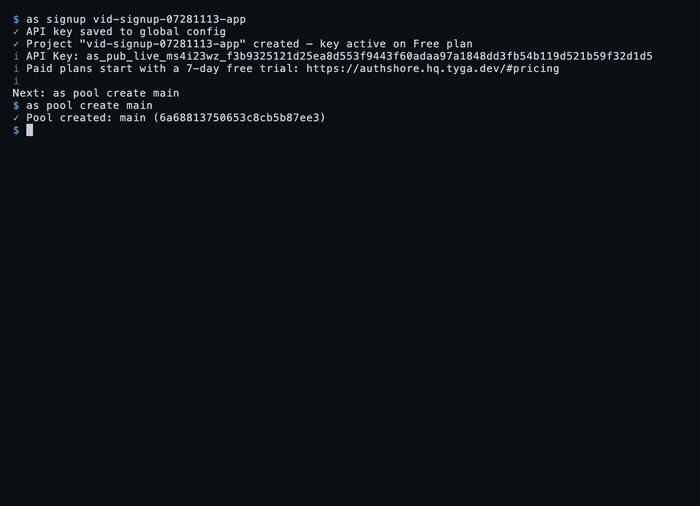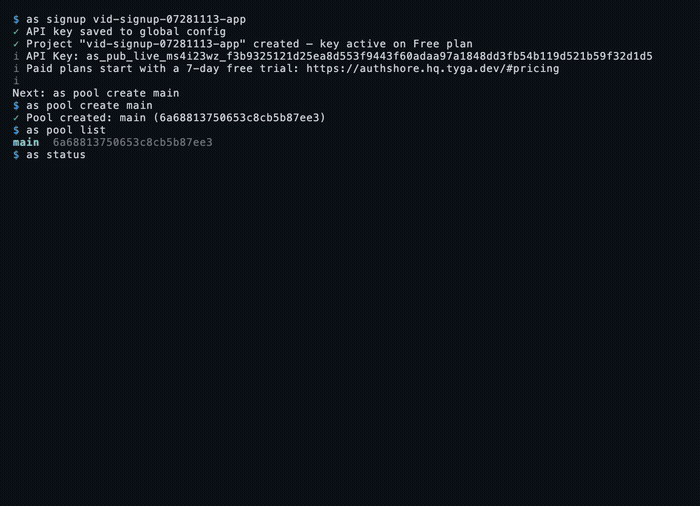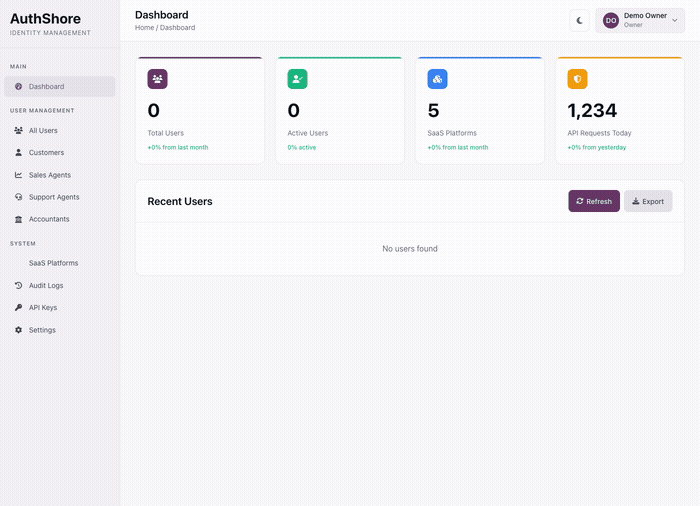
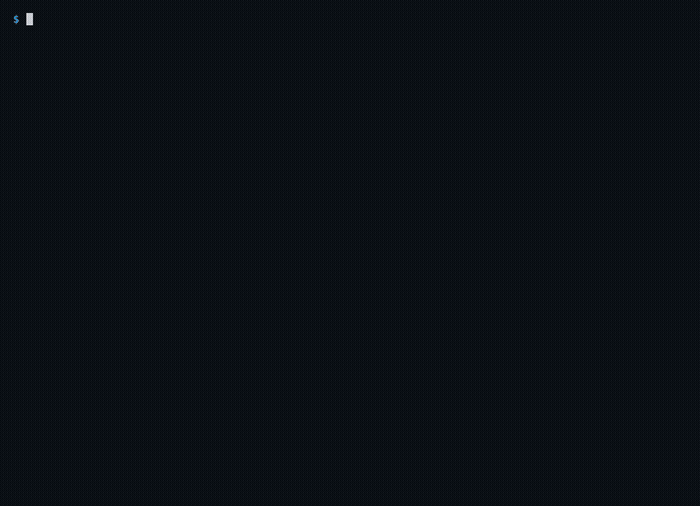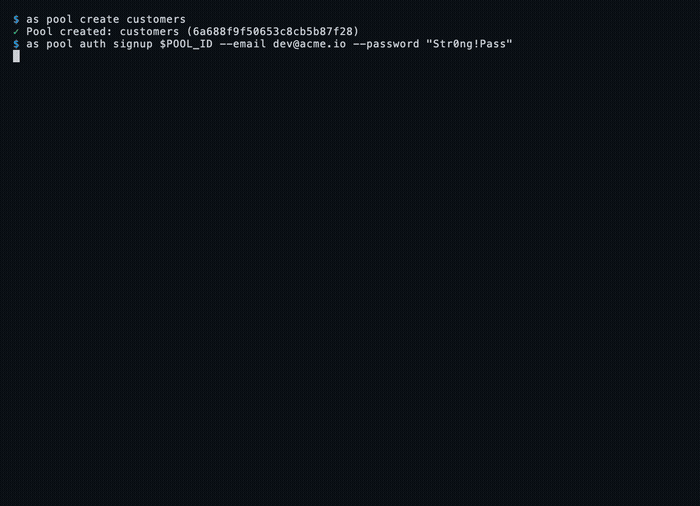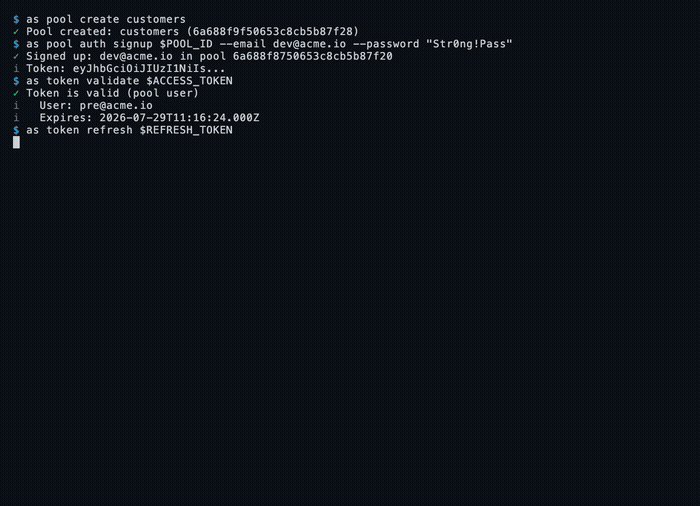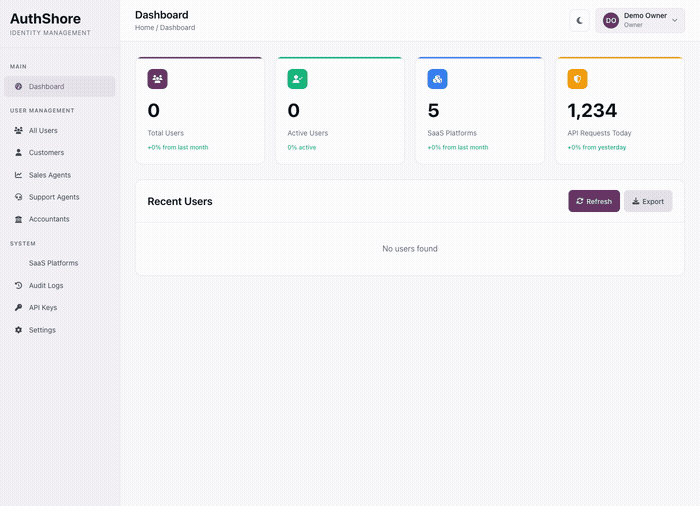
Real terminal sessions against the live API — click a GIF for the full video.
| Zero to auth in 60s | Secrets vault | Tokens & pools |
|---|---|---|
 |
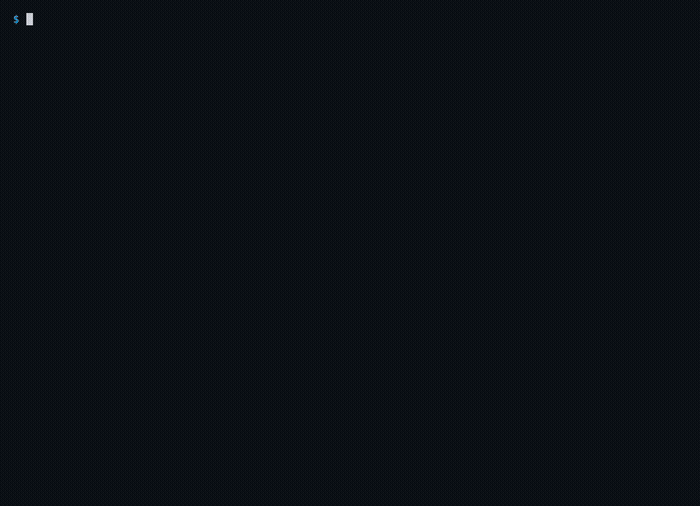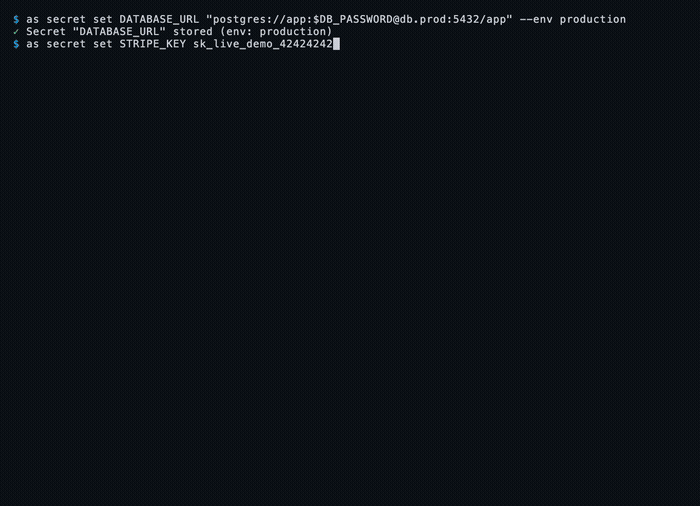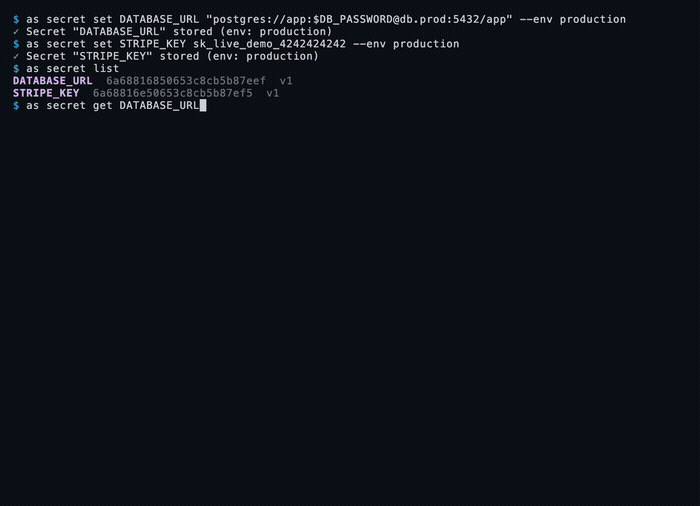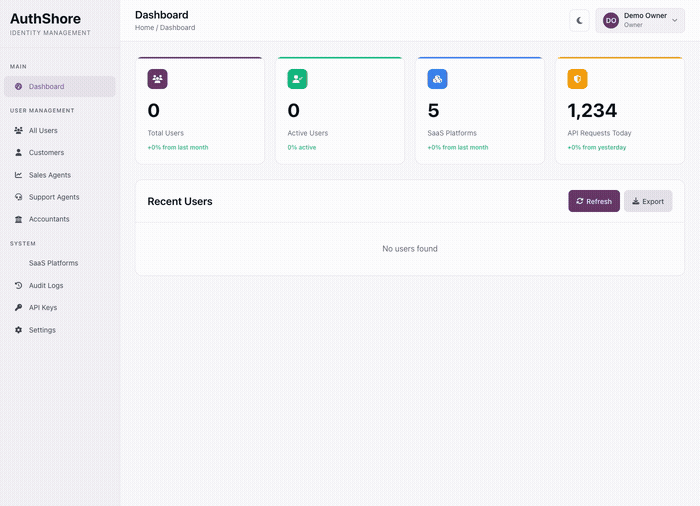 |
 |
More demos: authshore.ai/#demo
Install
npm install -g authshore
The npm package is authshore; the command is as.
Quick Start
# 1. Create a project — free plan, API key active immediately, no card
as signup my-project --email you@example.com --local

# 2. Create a user pool
as pool create main

# 3. Store a secret (encrypted at rest, versioned)
as secret set DATABASE_URL "postgres://user:pass@host:5432/db"

# 4. Sign up a user in your pool
as pool auth signup main --email user@example.com --password SecurePass123!

# Full reference
as help
User Pools — Cognito without the console
Every project gets isolated user pools your agent manages from the terminal: create pools, add users, run full signup/signin flows that return real JWT pairs.
as pool create main                      # create a pool
as pool list                             # list pools
as pool users <id>                       # list users in a pool
as pool user add <id> --email E --password P
as pool auth signup <id> --email E --password P   # returns access + refresh tokens
as pool auth signin <id> --email E --password P
Secrets Vault — stop pasting keys into .env
Encrypted, versioned key-value storage scoped to your project. Your agent stores third-party keys once and reads them at deploy time — nothing sensitive left sitting in the repo.
as secret set STRIPE_KEY "sk_..." --env production
as secret get STRIPE_KEY                 # decrypted read
as secret list
as secret versions STRIPE_KEY            # full version history
as secret delete STRIPE_KEY
Tokens — mint, validate, refresh, revoke
The JWT plumbing agents usually hand-roll, done right once.
as token validate <jwt>                  # verify signature + expiry, show claims
as token refresh <refresh-token>         # rotate the pair
as token revoke <token>                  # kill a compromised token
MCP Server
Prefer tools over a CLI? as ships an MCP server. Point Claude Code (or any MCP client) at it and your agent gets 18 native tools: pools, users, secrets, tokens, project status.
claude mcp add authshore --env AUTHSHORE_API_KEY=as_your_key_here -- as mcp-serve
For clients that use a JSON config (Cline, Cursor, Windsurf), pass your API key via the AUTHSHORE_API_KEY environment variable. The MCP server runs outside your project directory, so it will not pick up .authshore/config.json:
{
  "mcpServers": {
    "authshore": {
      "command": "as",
      "args": ["mcp-serve"],
      "env": { "AUTHSHORE_API_KEY": "as_your_key_here" }
    }
  }
}
No key yet? as signup my-project --email you@example.com provisions one in seconds — free plan, no card.
Remote MCP — zero install
No CLI at all? Claude Web, Claude Desktop, Raycast, or any hosted MCP client can connect straight to our remote server. Same 18 tools, nothing to install:
URL:  https://mcp.authshore.ai/sse
Auth: Authorization: Bearer YOUR_API_KEY
No key? Connect without one: the remote server starts in onboarding mode with an authshore_signup tool that provisions your account and unlocks everything in the same session.
Features
- User pools - isolated pools per project, full signup/signin flows, real JWT pairs
- Secrets vault - encrypted at rest, versioned, environment-scoped
- Tokens - validate, refresh, revoke from the terminal
- MCP server - 18 tools, local (
as mcp-serve) or fully remote (mcp.authshore.ai): Claude Code, Claude Web, Cursor, Raycast, any MCP client - Agent-first CLI -
--jsonon every command for programmatic parsing - Project-local config -
.authshore/config.json, auto-loaded, gitignore-friendly
Pricing: free plan with an instantly-active API key — no card, no trial clock. Paid plans (Starter $9 / Pro $29 / Scale $99 per month) come with a 7-day free trial via secure Stripe checkout. Details.
Config
as login --key YOUR_KEY --local     # saves to .authshore/config.json (project-local)
as config                           # show active config
as me                               # identity check: which project am I?
API key is resolved in this order (highest priority first):
--keyflagAUTHSHORE_API_KEYenvironment variable./.authshore/config.json(project-local)~/.authshore/config.json(global)
Add .authshore/ to your .gitignore.
Agent Integration
Add to your CLAUDE.md, .cursorrules, .clinerules, .windsurfrules, or AGENTS.md:
## Auth
This project uses AuthShore for auth: user pools, secrets, tokens.
Use the `as` CLI. Config is in .authshore/config.json (auto-loaded).
If not configured: as login --local --key YOUR_KEY
Run `as help` for the full command reference. Run `as me` before any writes.
Why this exists
Every agent-built app hits the same wall: auth. I watched my agents hardcode secrets, reinvent JWT refresh, and stall on Cognito consoles they can't click. So I built the auth layer the agent runs itself. It's early and I'm iterating fast: if something's rough or missing, open an issue — I read every one.
Documentation
License
Proprietary - Tyga.Cloud Ltd. See LICENSE.
推荐服务器

Baidu Map
百度地图核心API现已全面兼容MCP协议,是国内首家兼容MCP协议的地图服务商。

Playwright MCP Server
一个模型上下文协议服务器,它使大型语言模型能够通过结构化的可访问性快照与网页进行交互,而无需视觉模型或屏幕截图。

Magic Component Platform (MCP)
一个由人工智能驱动的工具,可以从自然语言描述生成现代化的用户界面组件,并与流行的集成开发环境(IDE)集成,从而简化用户界面开发流程。

Audiense Insights MCP Server
通过模型上下文协议启用与 Audiense Insights 账户的交互,从而促进营销洞察和受众数据的提取和分析,包括人口统计信息、行为和影响者互动。

VeyraX
一个单一的 MCP 工具,连接你所有喜爱的工具:Gmail、日历以及其他 40 多个工具。

graphlit-mcp-server
模型上下文协议 (MCP) 服务器实现了 MCP 客户端与 Graphlit 服务之间的集成。 除了网络爬取之外,还可以将任何内容(从 Slack 到 Gmail 再到播客订阅源)导入到 Graphlit 项目中,然后从 MCP 客户端检索相关内容。

Kagi MCP Server
一个 MCP 服务器,集成了 Kagi 搜索功能和 Claude AI,使 Claude 能够在回答需要最新信息的问题时执行实时网络搜索。

e2b-mcp-server
使用 MCP 通过 e2b 运行代码。

Neon MCP Server
用于与 Neon 管理 API 和数据库交互的 MCP 服务器

Exa MCP Server
模型上下文协议(MCP)服务器允许像 Claude 这样的 AI 助手使用 Exa AI 搜索 API 进行网络搜索。这种设置允许 AI 模型以安全和受控的方式获取实时的网络信息。